
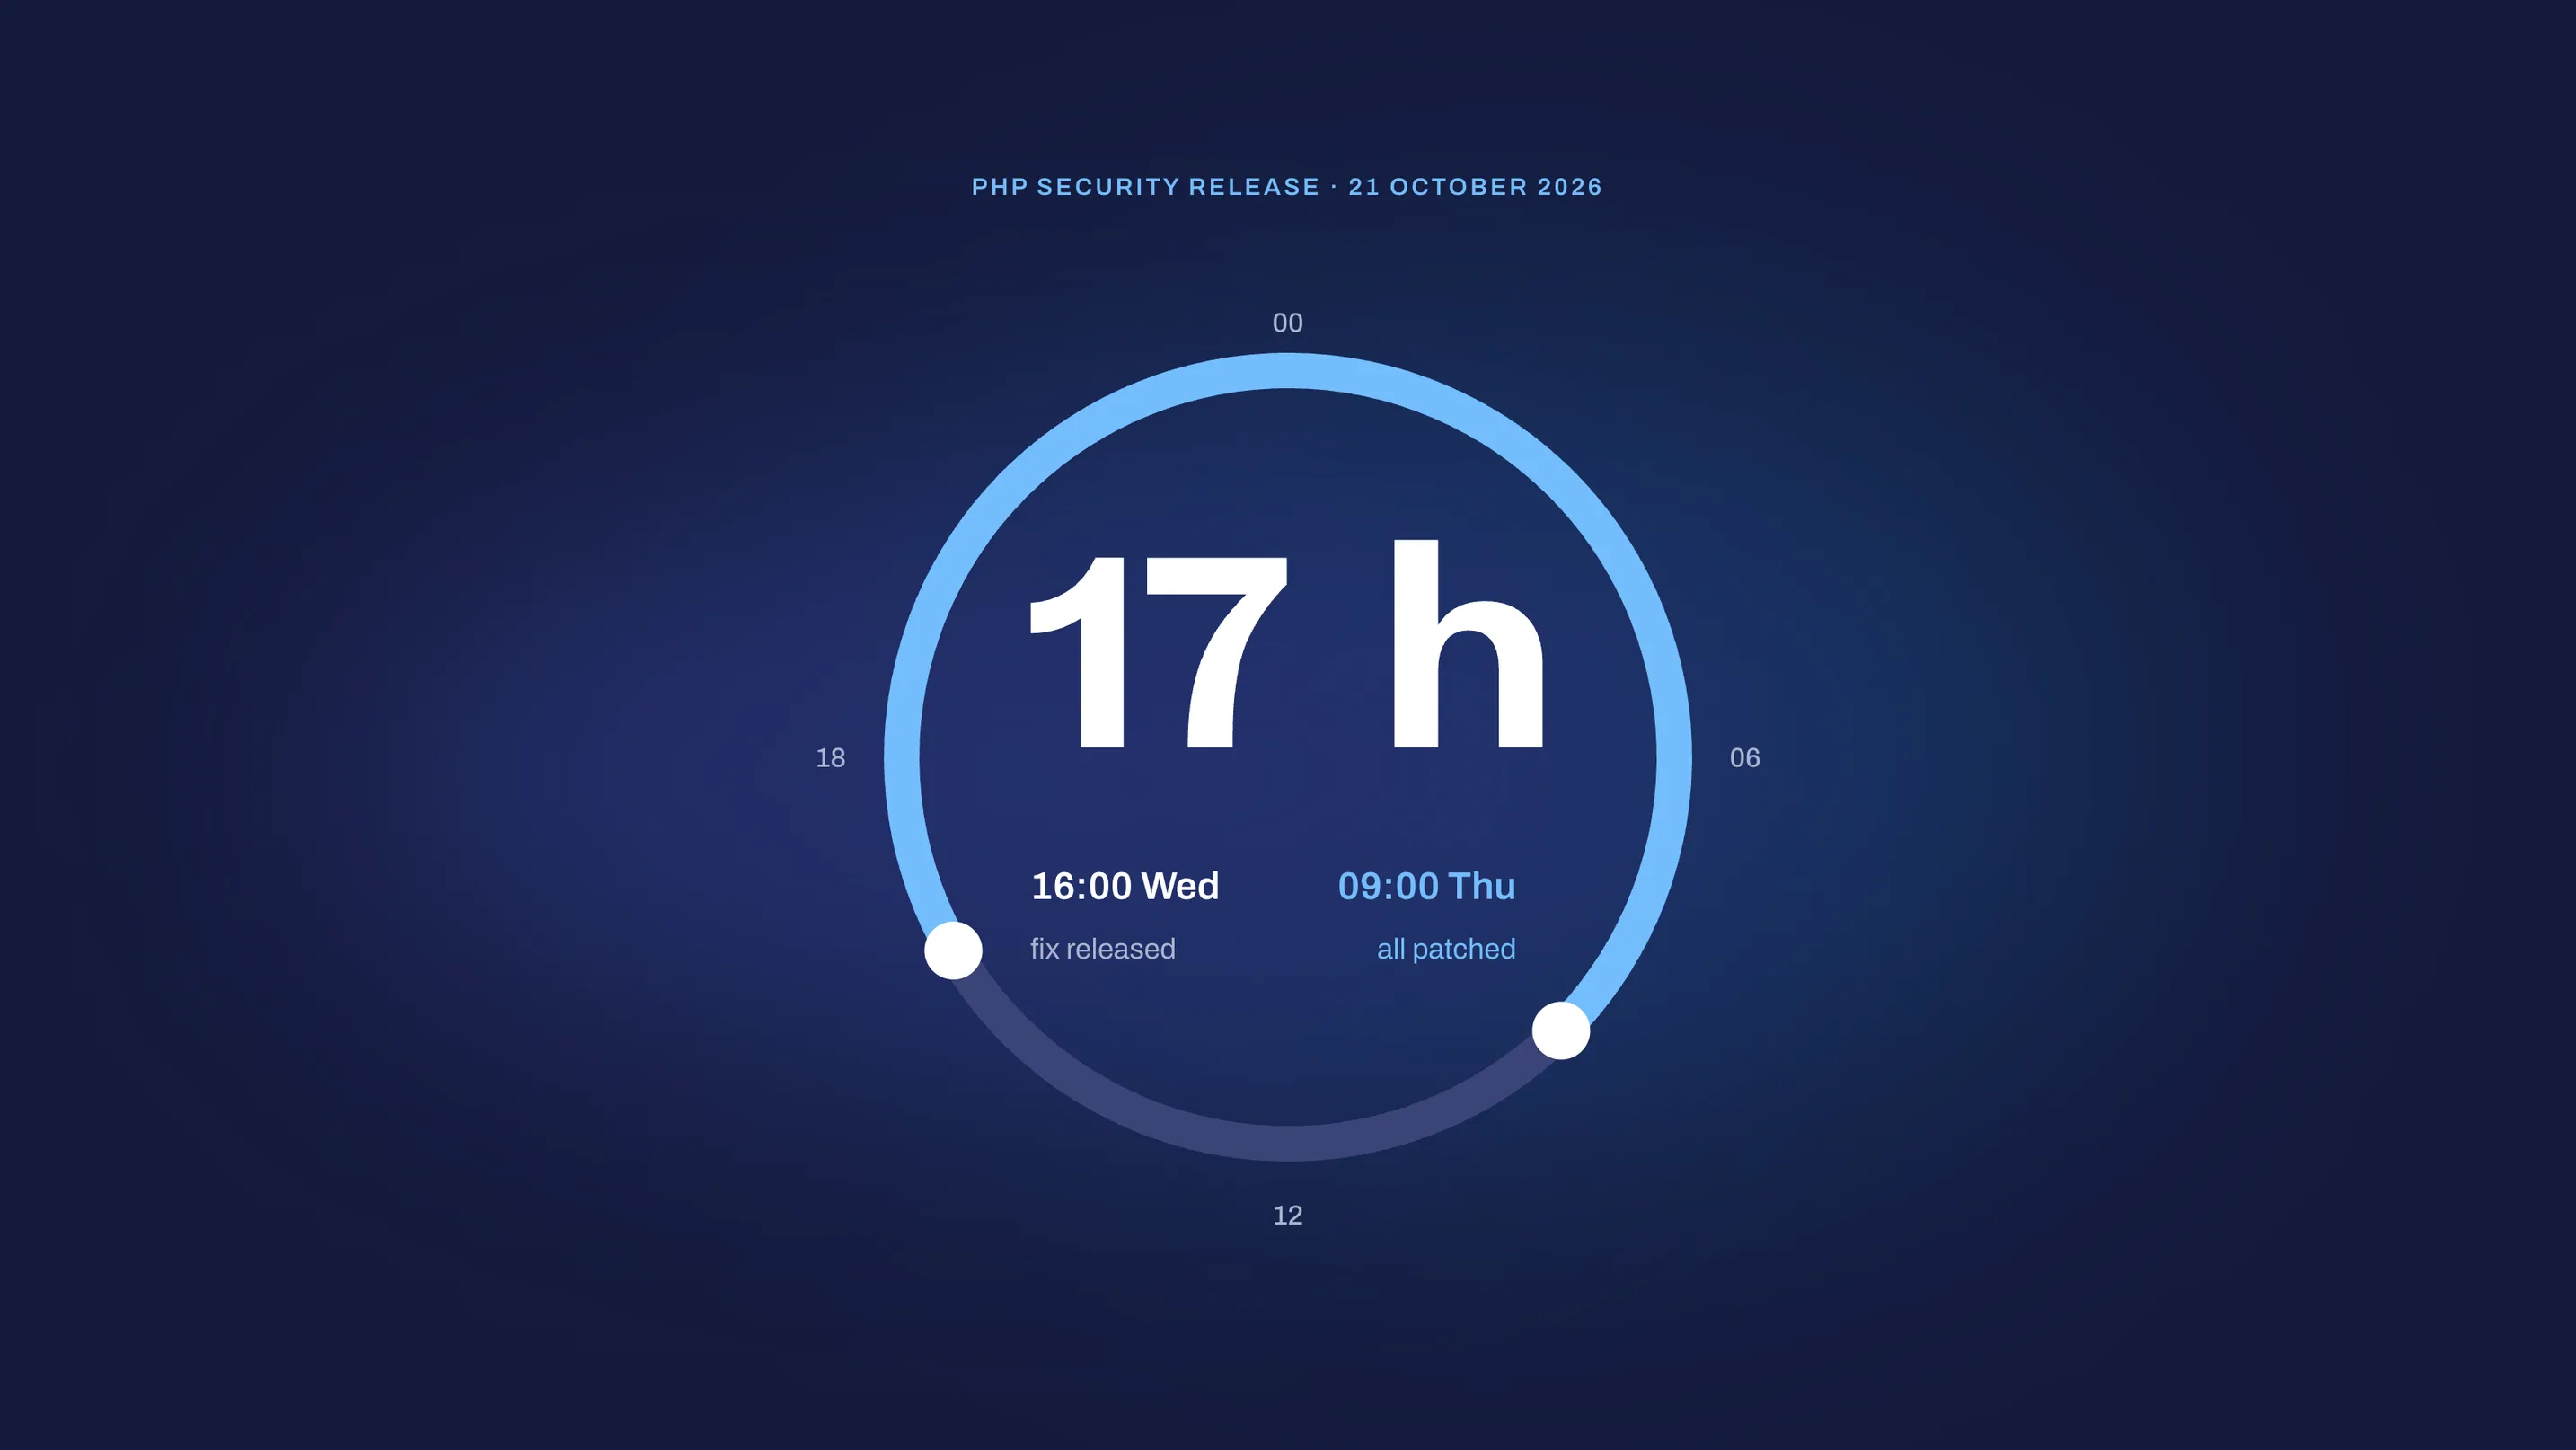
PHP released a critical security fix on Wednesday 21 October at 16:00. By 9:00 the next morning, every NWT client running PHP was patched.
The news
On 21 October, PHP released emergency updates for two critical vulnerabilities (CVE-2026-109618 and CVE-2026-109619). Under certain conditions, both let an attacker run code on a web server without logging in. PHP runs roughly 70% of websites with a known server-side language, according to W3Techs, including all Magento/Adobe Commerce and Shopware stores. This affected almost everyone.
The consequences
Timing is the key detail. A security update fixes a flaw and also shows where the flaw was. Once the fix is public, attackers study the changes, work out how to exploit them, and scan for sites that haven’t updated. That happened here. Within five days, the US Cybersecurity and Infrastructure Security Agency confirmed active attacks.
PHP gave one day’s warning but released the fix only at the announced time. Every unpatched store became a target the moment the fix went out. Checkout, customer data and order flows all sit on the same server as the vulnerable code.
How we handled it
When the release went out:
The first client was patched by 19:00 on Wednesday, three hours after release.
Every PHP client was patched before 9:00 on Thursday.
That is a fully patched client base within 17 hours of public release.
This speed comes from routine. We know our clients’ environments, we monitor releases, and we have a process ready for this kind of afternoon. When the next one lands, the work is execution.
What you should do now
If you run a PHP-based store, ask whoever maintains it: “Was the 21 October PHP security update installed, and when?”
Treat an unclear answer as a no. If the update went in days later, ask what happened in between. If your store runs PHP 8.1 or older, no official fix exists, and upgrading PHP is now urgent.
We can check your store, apply the fix, and take over security updates going forward on any platform. You can keep your current agency for everything else.
Questions about this vulnerability or where your store stands?


